



A vulnerability in Optimizely’s Web Experimentation product exposed visitors to the websites of 178 organisations to malicious code designed to redirect cryptocurrency payments to attackers’ wallets. The incident shows how hackers can steal digital assets without breaking into a blockchain.
The attack, discovered on November 16, affected organisations including Zoom, the BBC, HSBC, Ledger, CNN, Salesforce and IKEA. According to cybersecurity monitoring firm Report URI, the attacker injected malicious JavaScript into customer projects on Optimizely’s platform, so the code reached visitors through scripts that the websites already loaded.
The script replaced legitimate wallet addresses with ones controlled by the attacker. It altered addresses shown on webpages, copied to clipboards and sent in outgoing requests, so payments could be redirected without users noticing.
Report URI estimated that the attacker had received about $7,040 by 19:25 UTC on November 16. Technext’s review of the identified wallets on the morning of November 17, found activity the estimate didn’t capture.
The blockchain was not hacked, the websites using Optimizely were
The attackers did not need a flaw in Bitcoin, Ethereum or any other network. They targeted the software that displays information to website visitors.
Optimizely provides tools that let businesses test versions of their websites and personalise content. Customers add its JavaScript snippets to their sites, so compromising that code can reach visitors even when the sites themselves were never breached.
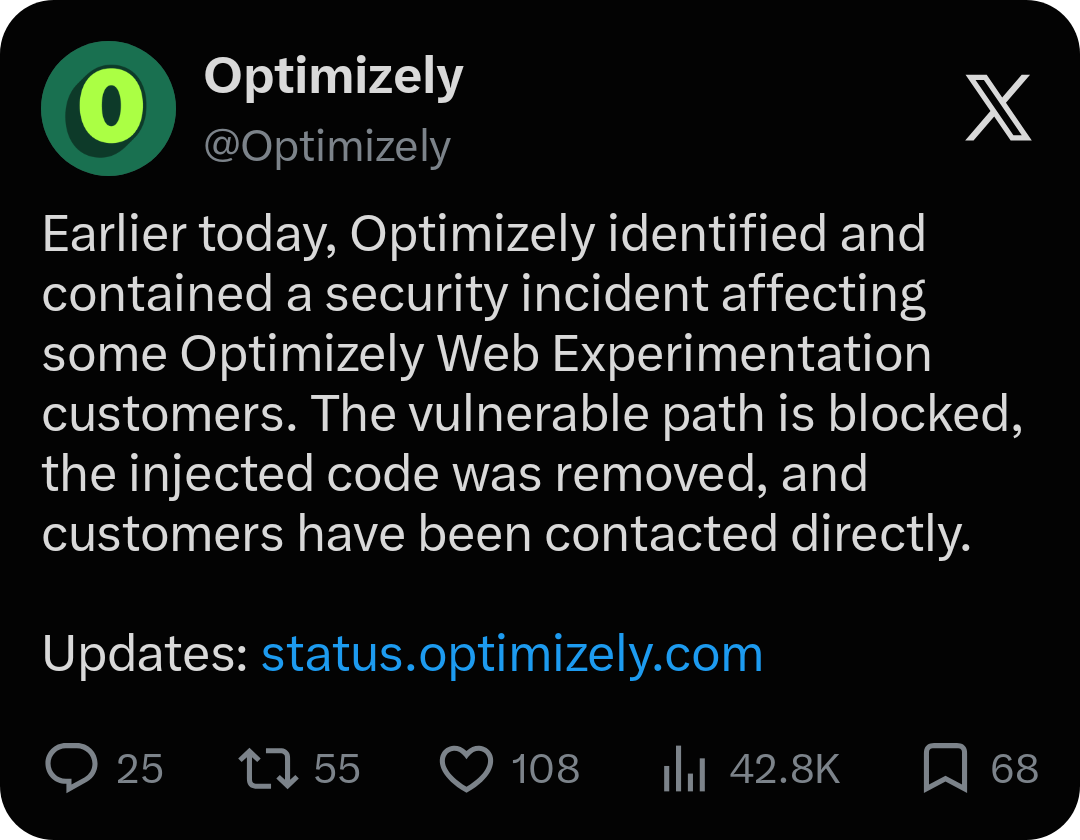
Optimizely acknowledged the incident in a security notice on November 17. The company disclosed that an unauthorised party had exploited a vulnerability in its Experimentation product to add malicious JavaScript to some customer projects. It added that it had fixed the flaw, removed the injected code, secured affected user accounts and added protections against unauthorised code delivery.
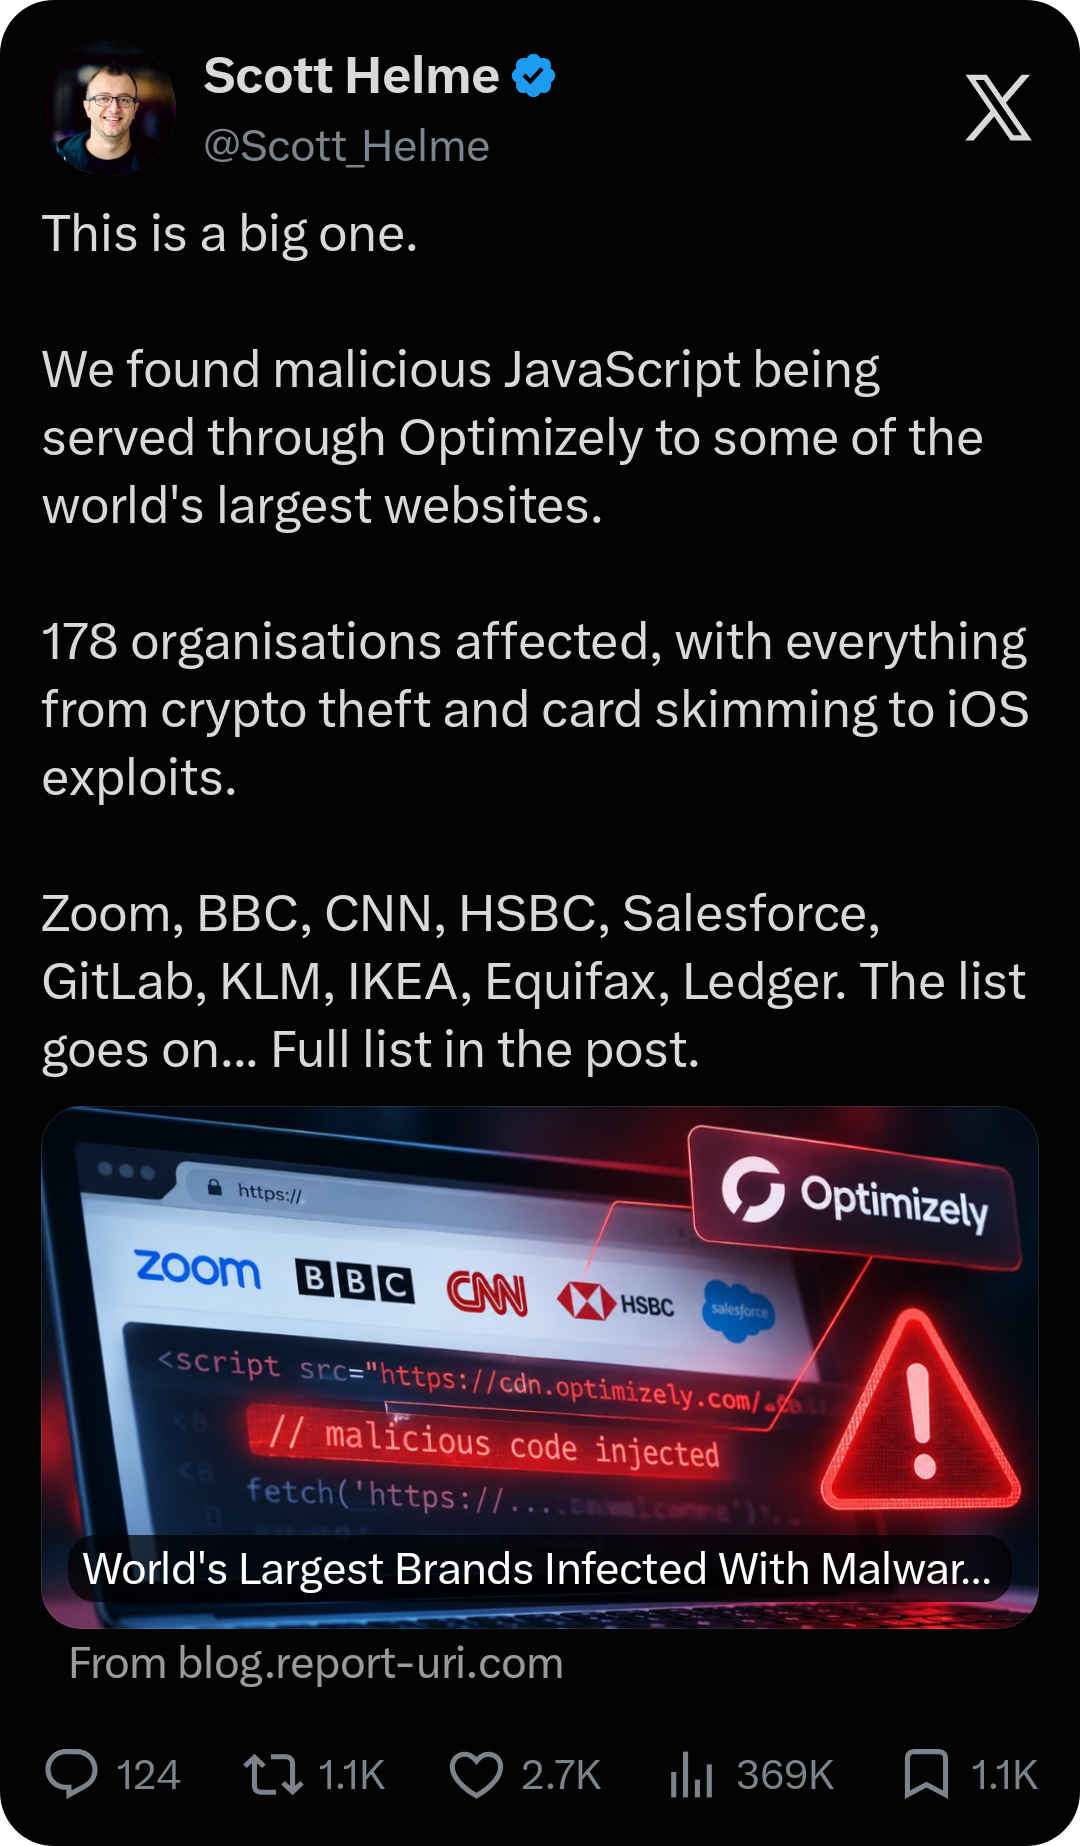
Cryptocurrency was only one part of the campaign. Report URI also found code built to capture payment card details, steal cookies and screenshots, and deliver iOS exploit kits to certain iPhones and iPads. It examined 1,611 Optimizely snippets, found 188 infected snippets belonging to 178 organisations, and cautioned that the real number could be higher. The count does not show how many visitors were exposed or how much money was lost.
What happened to the stolen cryptocurrency?
Public blockchains let researchers watch funds enter and leave identified wallets. Report URI’s Bitcoin (BTC) wallet had four deposits totalling 0.08298 BTC, about $5,380 at the time. Its other identified wallets received Litecoin, Tether (USDT), Tron (TRX), Ethereum and Binance Smart Chain assets.
Technext checked the wallets on public explorers:
- Bitcoin: five deposits totalling 0.08528782 BTC, one more than Report URI counted. The extra deposit was 0.00231063 BTC, roughly $150. The whole balance was then moved out shortly before Technext’s check.
- Tron: the wallet held less than $0.01 but was still showing transactions that morning. Many incoming transfers were tiny and the wallet held several spam tokens, so they cannot be treated as victim payments.
- Ethereum: the balance was close to zero, with outgoing transfers including USDC, the latest minutes before the check.
- Solana, Bitcoin Cash and Dogecoin: the Solana address does not exist on-chain, and the Bitcoin Cash address has no transactions, while the Dogecoin address returned no record on Blockchain.
- TON: zero balance, with one incoming transfer about 14 hours earlier from an address labelled traddergift.ton. The amount was not visible.
Technext did not check the Litecoin wallet.
An emptied wallet does not prove nobody tried to send funds to it, and an active one does not reveal how much was stolen. The extra Bitcoin deposit shows that the first transaction count was not final, but without tying further deposits to the script, calling it a confirmed increase in stolen funds would be premature. The $7,040 figure was Report URI’s estimate at one point in time, not a final tally.
The blockchain shows where funds moved. It cannot show who controls each address, how many victims were affected or whether the money was converted into cash.
Read also: 207 crypto hacks were recorded in H1 2026 as total stolen funds drop by 57% to $972 million
What Nigerian crypto users should check
No Nigerian organisation appears in Report URI’s published list, and HSBC Egypt is the only African entity named. The lesson for Nigerian users is about habit, not exposure to this specific attack.
Many people send USDT by copying an address from an exchange, payment page or merchant site and pasting it into a wallet app. Malicious JavaScript can swap the address in between. Confirmed transfers are generally irreversible, and there is no bank to call.
Users can reduce the risk in four ways:
- After pasting, compare the full address with the recipient’s original details, not just the first and last characters.
- Check that the network (TRON, Ethereum or another) matches the recipient’s instructions.
- For large transfers, send a small test amount first and confirm receipt independently.
- Get the recipient’s address through a separate channel where possible, such as a direct message, and compare it with the one the website shows.
Also read: Crypto hacks plunged 90% to $68.3 million in May, but the threat is far from over
